What Happened: 123GB of Business Contact Data Exposed
On November 5th, 2018, HackenProof discovered an unprotected MongoDB database sitting open on the internet—no password, no authentication, accessible to anyone who found it. The database contained 9,376,173 records totaling 123GB, including company information, employee contact details, job titles, phone numbers, email addresses, and internal "confidence scores" for each contact.
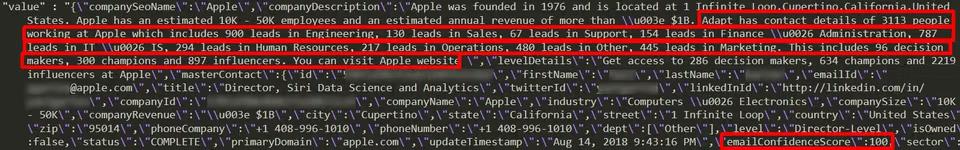
While each data point might look unremarkable on its own—a name, a title, a work email—having millions of them sitting in an unrestricted, publicly accessible database is exactly the kind of exposure that data protection regulations exist to prevent. Under GDPR, this class of violation can carry fines of up to €20 million or 4% of a company's annual global turnover, whichever is greater.
Who Owns the Data?
The exposed database originated from Adapt.io, a service that provides access to business contact and company data for sales and marketing teams. Based on the nature of the exposure, this looks like a misconfiguration rather than an intentional disclosure—the kind of mistake that happens when a database is spun up quickly, and authentication is left as an afterthought. HackenProof attempted responsible disclosure and reached out to Adapt.io directly, but received no response.
The Have I Been Pwned Upload
Following the discovery, the 9.3 million exposed email addresses were uploaded to Have I Been Pwned, Troy Hunt's widely used breach-notification service. Anyone whose work email was in the exposed database can check whether they were affected by searching their address there.
Is Adapt.io Still Safe to Use? What Buyers Should Know
Adapt.io is still an independently operating company today, and it's grown considerably since 2018—the platform now advertises access to over 250 million business contacts, well beyond the scale of the 2018 exposure. There's no public record of a further breach since this incident, and the company continues to be actively marketed and reviewed as a budget-friendly B2B contact database (it currently holds a 4.6/5 rating on G2 across thousands of reviews).
That said, "no further public breaches" isn't the same as "verified secure." If you're evaluating Adapt.io—or any B2B data vendor—as part of your sales or marketing stack, it's worth treating this history as a prompt to ask the vendor directly about their current security posture, not as a reason to avoid the category entirely. Every company that stores contact data at scale is a target; the difference is whether they can show you how they're defending it.
How to Vet a B2B Data Vendor's Security Practices
Before connecting any third-party contact database to your CRM or sending it your prospect lists, a few questions are worth asking upfront:
- Does the vendor run a bug bounty program or commission regular third-party security audits? A vendor with nothing to show here is asking you to take their security on faith.
- Has the vendor disclosed any past breaches, and how did they respond—quickly and transparently, or only after public pressure?
- Is their infrastructure encrypted at rest and in transit, and do they publish a security or trust page?
- Are they GDPR- and CCPA-compliant, with a documented process for data subject requests and deletion?
- Do they restrict internal access to production databases, and can they describe their access-control model if asked?
This is the same due-diligence lens we'd recommend applying to your own infrastructure—see our Kars4Kids breach report for another example of how an unprotected MongoDB instance turned into a real-world exposure, and how a managed bug bounty platform helps catch these misconfigurations before they go public.
Adapt.io Data Breach: FAQ
What data was exposed in the Adapt.io breach?
An unprotected MongoDB database exposed 9,376,173 business contact records (123GB total), including company details, employee names, job titles, phone numbers, email addresses, and internal confidence scores.
Did Adapt.io respond to the disclosure?
No. HackenProof attempted responsible disclosure directly with Adapt.io but received no response at the time.
How can I check if my email was affected?
The 9.3 million exposed email addresses were uploaded to Have I Been Pwned—you can search your email address there to check.
Is Adapt.io still safe to use today?
Adapt.io remains an active, independently operating company with no public record of further breaches since 2018. As with any data vendor, it's reasonable to ask directly about their current security practices—including bug bounty coverage and audit history—before connecting it to your own systems.